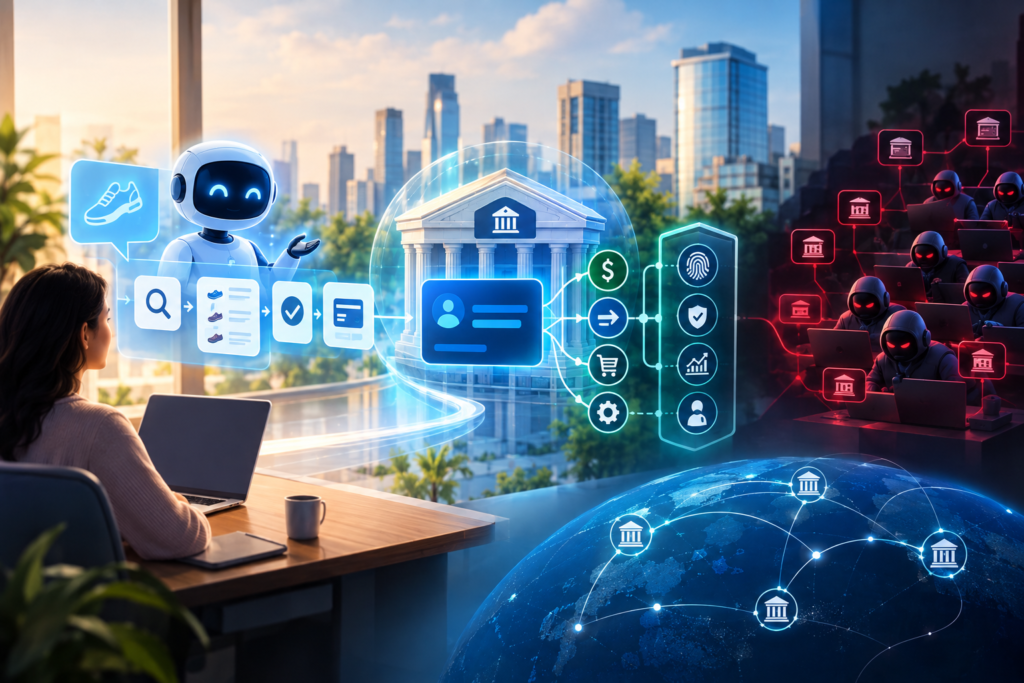
Agentic payments are moving from an interesting concept to an important part of the future of commerce. An AI agent can understand a customer’s intent, search for the right product or service, evaluate options, initiate a transaction and, within defined permissions, complete the payment without requiring a human to intervene at every step. The attraction is obvious. Consumers can delegate routine financial decisions, businesses can automate purchasing and expense processes, and merchants can interact with software that is capable of completing a transaction rather than simply displaying an option. Payments can become less of a process that a person actively performs and more of an outcome that an agent executes on their behalf.
This is why banks, payment networks, fintechs and technology companies are investing heavily in agentic commerce. The objective is not simply to make payments faster. It is to remove friction from the entire commerce journey. An agent can continuously monitor a requirement, make a decision when the right conditions are met and execute the resulting payment. With appropriate authentication, authorization, transaction limits, human approval thresholds and monitoring, this can create a powerful new model of financial interaction. In that context, giving an agent access to an existing bank account can seem like only the beginning.
The natural next question is: why shouldn’t an agent be allowed to open a bank account as well?
The argument is easy to make. An autonomous business agent may need an account to manage its own expenses. A financial agent may need a dedicated account to manage a budget. A purchasing agent could establish payment relationships without requiring a human to complete every onboarding step. If the objective of agentic commerce is genuine autonomy, requiring a human to manually open every financial account becomes an obvious point of friction.
But a bank account is fundamentally different from a payment authorization. An account is not merely another credential that allows money to move. It is a financial identity. It can receive funds, originate transactions and establish relationships with other accounts and financial institutions. Opening an account therefore does more than give an agent permission to act. It potentially gives an autonomous system a financial presence.
That distinction becomes particularly important when we consider the mule-account problem.
Financial institutions already invest enormous resources in identifying accounts that are being used to receive, move or facilitate illicit funds. The controls around onboarding, KYC, AML, transaction monitoring, behavioral analytics and fraud detection are designed around identifying suspicious identities and patterns of financial activity. These controls are continuously evolving, but they operate within a world where the underlying actors are predominantly people and organizations.
Now introduce autonomous systems into that environment.
The concern is not necessarily that an AI agent will independently decide to become a criminal. The more significant concern is that an adversary could use autonomous systems to automate and scale activities that currently require substantial human effort. If software can interact with onboarding processes, create applications, operate accounts, initiate transactions and adapt its behavior based on the responses it receives from financial controls, the problem is no longer simply automated fraud. It becomes an autonomous system interacting with another automated system.
This changes the security equation.
The traditional model has largely been:
Human attacker → automated financial system → detection controls
The emerging model could become:
Autonomous system → automated financial system → autonomous detection system
That is a fundamentally different environment. The defender is no longer necessarily detecting a human operating through a relatively predictable set of constraints. The adversary may also be capable of automation, experimentation and adaptation. A static bot can be detected and blocked. An autonomous system that can modify its behavior in response to controls presents a much more difficult problem.
This is where the potential scale of the mule-account problem becomes particularly concerning. Today, creating and operating financial identities at scale involves practical constraints: people, devices, time, operational processes and the ability to respond to verification and monitoring. Autonomous systems could potentially reduce some of those constraints. Even if individual accounts are detected and closed, the economics and speed of creating new identities could change the nature of the problem. The issue is therefore not simply whether an individual AI-created account can be identified as suspicious. It is whether the financial ecosystem is prepared for potentially coordinated, adaptive and machine-scale financial identities.
This does not mean that autonomous agents should simply be excluded from financial systems. The benefits of agentic commerce are too significant, and legitimate use cases will continue to grow. The more important question is how an agent should participate in the financial system.
One possible distinction is between account ownership and delegated financial authority. An AI agent does not necessarily need to become an independent customer in order to perform autonomous financial activity. It could instead have a verifiable machine identity and operate under explicitly delegated authority from a person or organization. That authority could define what the agent is permitted to do, which accounts it can access, transaction limits, permitted counterparties, spending purposes and when human intervention is required. Every action could remain attributable to both the agent and the entity that delegated the authority.
This creates a very different security model. Instead of treating an AI agent as another customer, the financial ecosystem can treat it as an accountable autonomous actor operating within a defined trust boundary. Identity, authorization, behavioral monitoring, transaction controls and revocation then become properties of the agent itself rather than assumptions inherited from the human behind it.
More importantly, this architecture needs to be considered before autonomous financial identities become widespread.
Financial security has historically evolved through a reactive cycle. A new attack emerges, institutions observe the behavior, detection mechanisms are developed, and controls are strengthened. That approach is already challenging when the adversary is human. It becomes even more difficult when the adversary can automate experimentation and adapt continuously to the defenses it encounters.
Agentic finance gives the industry an opportunity to break that cycle.
The industry can define agent identity standards, delegated authority models, machine-level authentication, behavioral monitoring, transaction-level policy enforcement, traceability and rapid revocation before autonomous account creation becomes commonplace. The objective should not be to prevent autonomy. It should be to make autonomy accountable, attributable and controllable.
The question facing payments is therefore not whether AI will participate in financial activity. It almost certainly will. The more important question is where the boundary of that participation should be drawn.
Giving an agent permission to make a payment is one thing.
Giving it the ability to create the financial identity from which that payment originates is something much bigger.
If we wait for the first large-scale autonomous abuse of financial identities to tell us where that boundary should be, we will already be designing from behind the problem.
The time to design the security model for autonomous financial identities is before the first autonomous mule account—not after it.